
What Are Web Cookies in 2026? How They Work, When Consent Matters, and 7 Live Checks
Teams researching what are web cookies usually do not need another generic privacy article. They need a practical read on how the controls behave on a live build, where the friction shows up, and what should be tested before a site ships.
The useful test for what are web cookies is not whether the banner looks finished. It is whether the live build blocks what it should block, records what it should record, and stays stable after ordinary releases.
That sounds simple because, technically, it is simple.
The real review is not simple anymore.
In 2026, a useful what are web cookies answer has to cover at least four things at once:
- what the cookie does;
- how long it lasts;
- whether it supports the service or supports tracking; and
- whether the live site respects the consent or opt-out choices it shows to people.
Current official guidance still points in that direction. MDN’s HTTP documentation explains that cookies are set with the Set-Cookie response header and usually sent back in the Cookie request header. The ICO’s finalized 2026 storage-and-access-technologies guidance says non-exempt technologies should not be pre-enabled and should be reviewed regularly. California’s Department of Justice still says businesses that sell or share personal information must honor a valid Global Privacy Control signal as an opt-out request where the law applies.
If you want nearby context first, start with these guides to browser cookies, what are website cookies, and cookie policy. This page stays a little broader. It is the what are web cookies explainer I would use this week before approving a banner, a privacy-policy update, or a runtime cookie audit.
If your team is trying to get what are web cookies under control without adding a heavyweight privacy stack, DataShyre can help. DataShyre focuses on consent and preference management that are easier to implement, easier to operate, and easier to trust on a live site. Start with DataShyre’s consent and preference management or book a demo.
If your team already knows the definitions but needs the site behavior to match the notice and controls, DataShyre can help connect the policy layer to the runtime reality through consent management, data mapping, and website privacy checker.
1. Web cookies are a browser memory mechanism
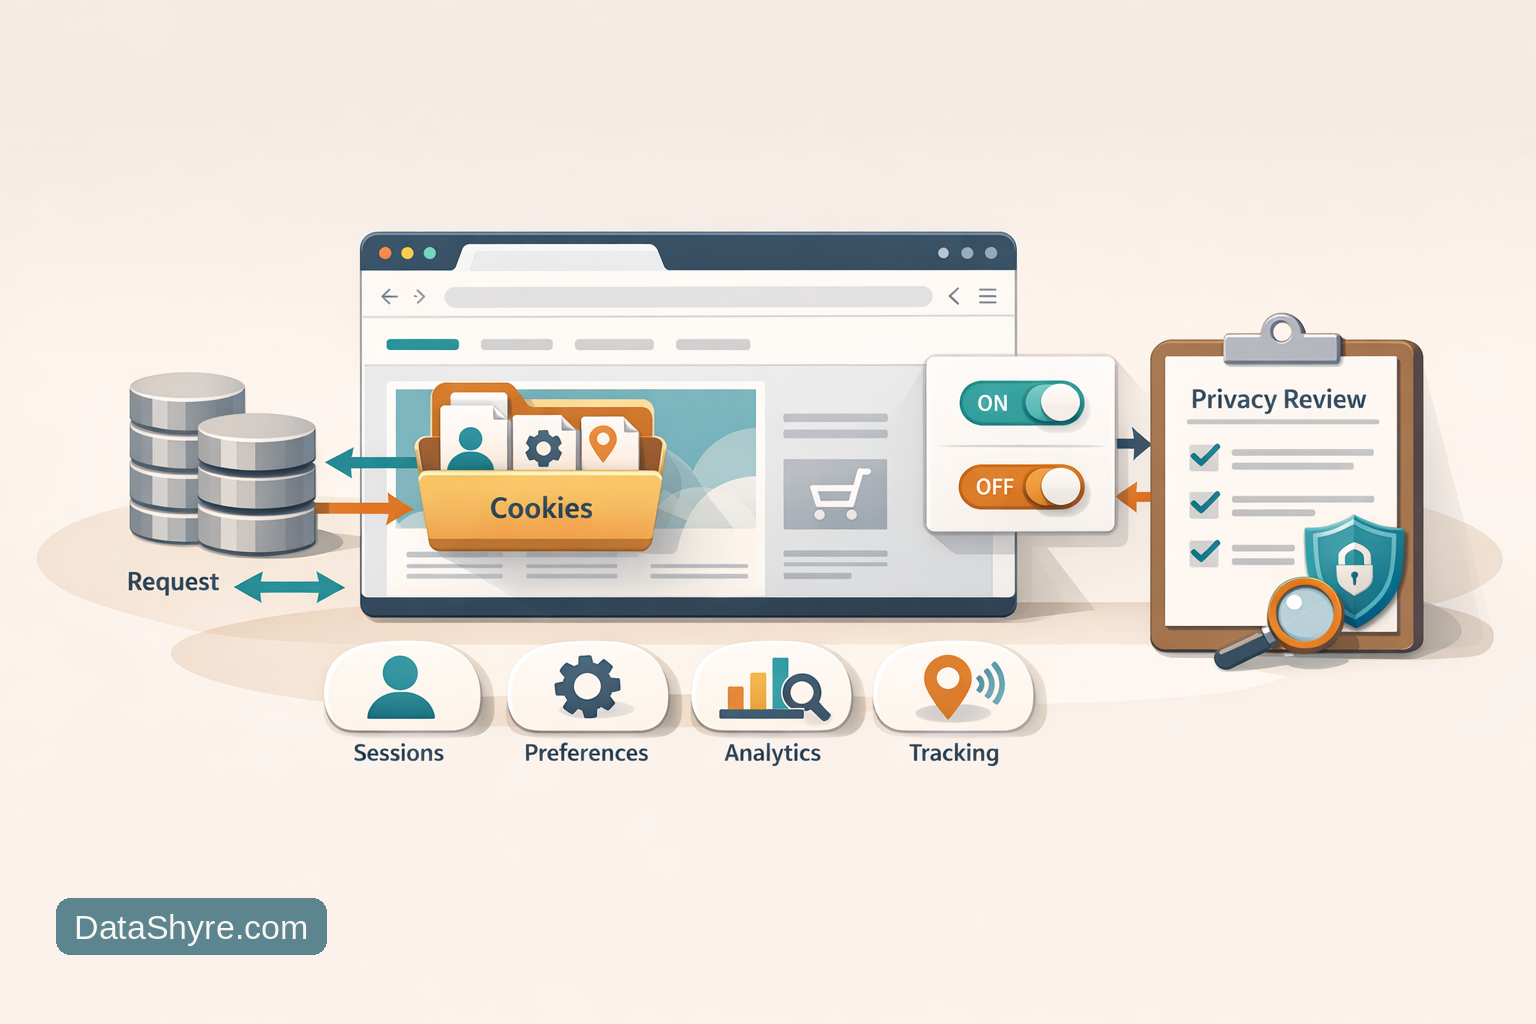
At the protocol level, web cookies are still straightforward.
A server can send a cookie to the browser, and the browser can send it back later when the right domain and path conditions are met.
That mechanism lets a site remember things like:
- whether a user is signed in;
- language or display preferences;
- shopping-cart state;
- security and session continuity; or
- analytics and advertising identifiers.
This is why the right follow-up question is not only does this site use cookies.
It is which cookies are doing which jobs.
Once you ask that question, what are web cookies stops being a definition-only topic and becomes an inventory and control topic.
2. Session cookies and persistent cookies create different risks
One reason people get confused about what are web cookies is that they imagine one generic kind of browser record.
In real deployments, lifetime matters.
MDN’s current guidance still distinguishes between session cookies, which usually disappear when the session ends, and persistent cookies, which use Expires or Max-Age and can stay longer.
That changes the review.
A short-lived session cookie used to keep a user authenticated is a different privacy and security object from a longer-lived identifier used for analytics or recognition across visits.
The ICO’s current compliance guidance also says duration should be proportionate and limited to what is necessary for the intended purpose.
So when a team asks what are web cookies, I would immediately ask:
- is the cookie session-only or persistent;
- why does it need that lifetime;
- does the duration still fit the purpose; and
- could the same user outcome be delivered with a shorter window.
3. First-party and third-party web cookies are not interchangeable
The phrase web cookies often hides an important distinction.
Some cookies are set in the context of the site a person believes they are visiting. Others may be set by embedded providers, ad-tech tools, social widgets, measurement platforms, or other third-party components.
Firefox’s current support guidance still describes third-party cookies as cookies set by a website other than the one a person is currently on, and says cross-site tracking cookies are disabled by default for Firefox users. Chrome’s current DevTools guidance still tells developers how to inspect third-party cookies and surfaces cookie fields such as SameSite, expiry, and partition key.
That matters because third-party or cross-site behavior usually creates the harder operational questions:
- who is receiving the identifier;
- whether the purpose is necessary or optional;
- whether the user saw a real choice first; and
- whether the browser is limiting, isolating, or treating that cookie differently.
This is why a strong what are web cookies review needs both a legal and a browser-runtime lens.
4. Consent depends on purpose, not on the word cookie by itself
Some articles answer what are web cookies as if all cookies always need consent.
Others answer as if cookies are always harmless.
Neither approach is good enough.
The ICO’s final storage-and-access-technologies guidance says that, unless an exception applies, consent is required before using non-exempt technologies and they must not be pre-enabled. The same guidance also makes clear that the review now covers more than classic cookies alone.
So the practical consent question is:
- is the cookie strictly necessary for the service the user requested;
- is it instead for analytics, advertising, personalization, or another optional purpose;
- is that optional behavior blocked until a valid choice is made; and
- can the person refuse or later withdraw as easily as they can accept.
That is where many banners fail live review.
They answer what are web cookies with friendly text while still dropping optional identifiers too early or making withdrawal harder than acceptance.
5. Web cookies are only part of the device-storage picture
A safer 2026 answer to what are web cookies also admits what cookies are not.
They are not the whole online-tracking story.
The ICO’s current guidance uses the broader category of storage and access technologies and says the PECR rules apply to any technology used to store or access information on a user’s device, including scripts, tags, and other methods.
That means a site can appear to use fewer classic cookies while still using:
- local storage;
- session storage;
- pixels or tags;
- embedded third-party scripts; or
- other device-side techniques that pursue similar measurement or profiling outcomes.
So when someone asks what are web cookies, the honest answer should not stop at the cookie table.
It should also ask what else is being stored, accessed, or triggered in the browser.
6. California adds an opt-out branch, not only a consent branch
For California-facing sites, what are web cookies is not only a cookie-banner question.
It can also be an opt-out and signal-recognition question.
California DOJ’s CCPA guidance still says that one acceptable method for online businesses to honor opt-out requests is via a user-enabled Global Privacy Control signal, and it still points consumers to privacy policies and rights workflows for how those requests are handled.
That matters because some web-cookie use cases can fall into sale or sharing analysis depending on what the identifiers enable and where the data goes.
So if your site uses optional advertising or cross-context measurement tooling, the live review should test:
- whether the required notice exists;
- whether the opt-out path is clear;
- whether GPC is honored where applicable; and
- whether downstream behavior changes after the signal or request.
That is a much more useful answer to what are web cookies than a generic small files in your browser definition.
7. The best answer is a live audit sequence
At this point, the most practical answer to what are web cookies is the one that helps your team test a real site.
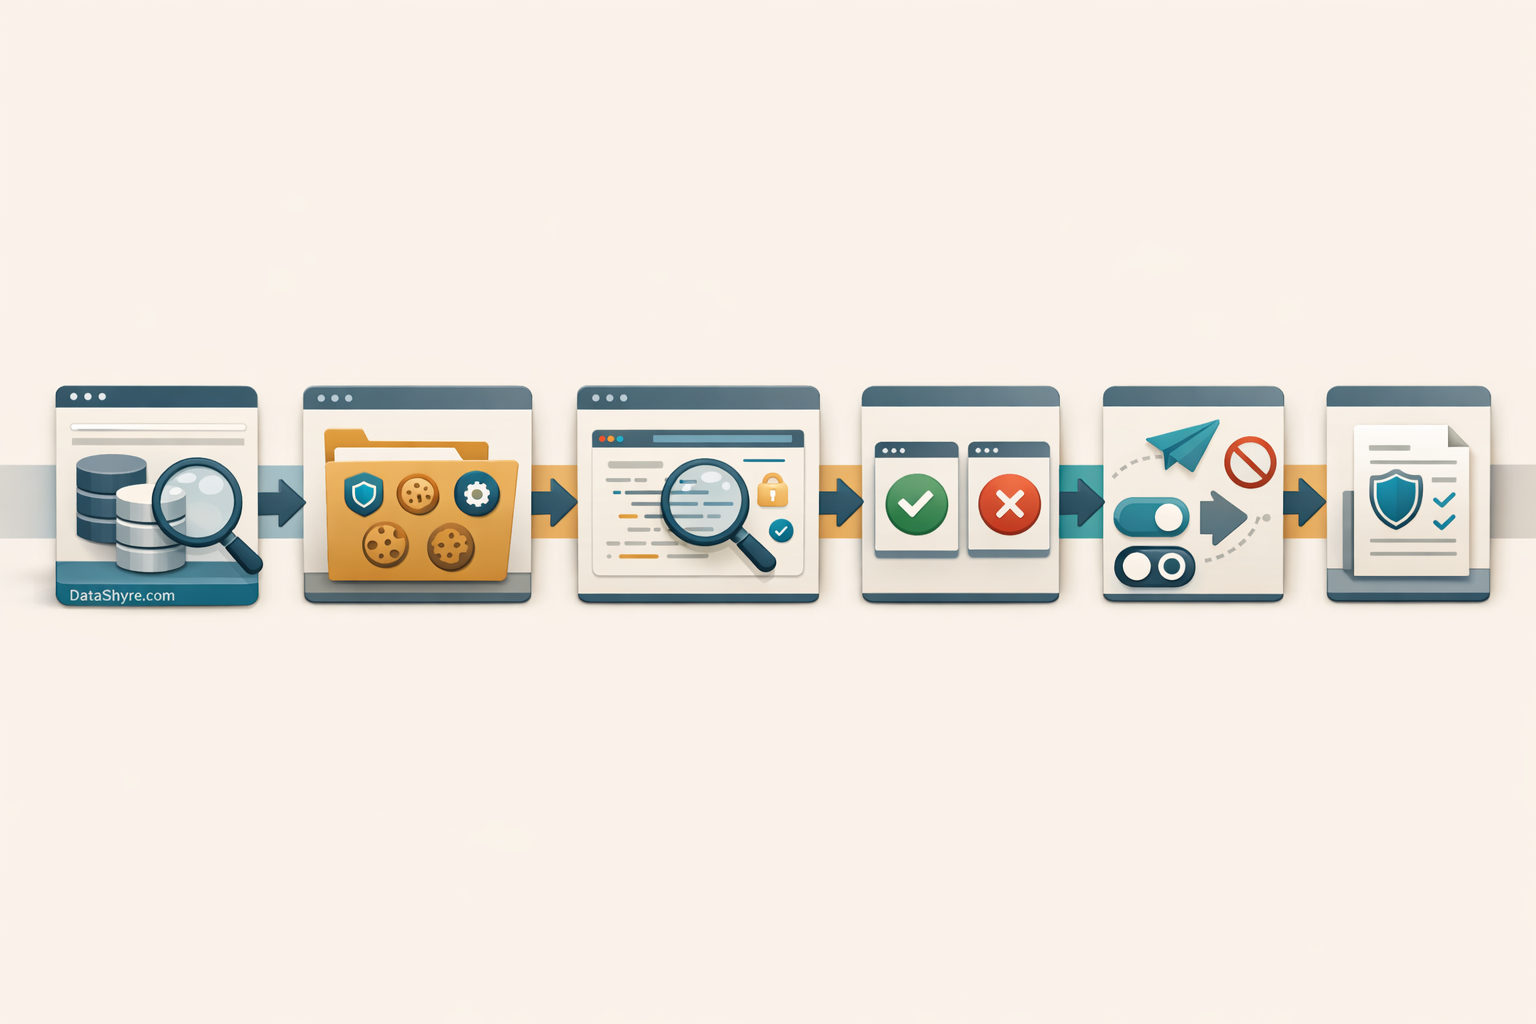
If I were auditing this week, I would use this order:
- identify every cookie and adjacent storage/access technology that appears before any user choice;
- classify each item as necessary, preference, analytics, advertising, or embedded-third-party behavior;
- inspect lifetime, domain, path,
Secure,HttpOnly, andSameSitehandling for the important cookies; - compare the no-choice, reject, and accept branches in the browser;
- test whether later withdrawal actually changes runtime behavior;
- test California opt-out and GPC handling where it applies; and
- compare the findings against the banner, privacy policy, and vendor inventory.
That sequence usually surfaces the truth faster than either a copied policy paragraph or a spreadsheet of cookie names alone.
FAQ
What are web cookies in simple terms?
They are small pieces of browser-stored data used to remember state, preferences, sessions, or identifiers between web requests.
Are web cookies the same as browser cookies?
Usually the terms point to the same underlying mechanism. Web cookies is the broader plain-language phrasing, while browser cookies emphasizes where the data is stored and inspected.
Do all web cookies need consent?
No. The answer depends on purpose and jurisdiction. Optional tracking often needs prior user choice, while strictly necessary functions may not. The safest workflow is to classify each cookie and test the live runtime instead of assuming one rule covers everything.
Bottom line
The best answer to what are web cookies in 2026 is not only small browser files.
It is small browser-side records whose compliance and privacy meaning depends on purpose, lifetime, browser behavior, and whether the user's choices actually change what happens next.
The practical test for what are web cookies is simple: if the site can explain the rule, enforce the choice, and keep that behavior stable through ordinary releases, the setup is moving in the right direction.
Sources
- MDN, Using HTTP cookies: https://developer.mozilla.org/en-US/docs/Web/HTTP/Guides/Cookies
- MDN, Secure cookie configuration: https://developer.mozilla.org/en-US/docs/Web/Security/Practical_implementation_guides/Cookies
- Chrome for Developers, View, add, edit, and delete cookies: https://developer.chrome.com/docs/devtools/application/cookies
- Firefox Help, Third-party cookies and Firefox tracking protection: https://support.mozilla.org/en-US/kb/third-party-cookies-firefox-tracking-protection
- ICO, Guidance on the use of storage and access technologies: https://ico.org.uk/for-organisations/direct-marketing-and-privacy-and-electronic-communications/guidance-on-the-use-of-storage-and-access-technologies/
- ICO, What are storage and access technologies?: https://ico.org.uk/for-organisations/direct-marketing-and-privacy-and-electronic-communications/guidance-on-the-use-of-storage-and-access-technologies/what-are-storage-and-access-technologies/
- ICO, How do we comply with the PECR rules?: https://ico.org.uk/for-organisations/direct-marketing-and-privacy-and-electronic-communications/guidance-on-the-use-of-storage-and-access-technologies/how-do-we-comply-with-the-pecr-rules
- California Department of Justice, California Consumer Privacy Act (CCPA): https://oag.ca.gov/privacy/ccpa
- WordPress Developer Handbook, Suggesting text for the site privacy policy: https://developer.wordpress.org/plugins/privacy/suggesting-text-for-the-site-privacy-policy/